Speakers
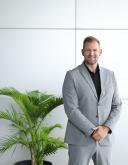
Martin Kofoed Høding, VP of Cybersecurity & CISO, SAS – Scandinavian Airlines
Martin Kofoed Høding is Vice President of Cybersecurity and Chief Information Security Officer (CISO) at SAS – Scandinavian Airlines. With a technical background and experience as a former police superintendent, he spent 10 years in law enforcement, including in the early days of the Danish National Cybercrime Centre (NC3), where he led Digital Forensics and High-Tech... Crime investigations units. From 2015, he led operational cybersecurity, crisis management, and incident response efforts at JN Data, and later served as Partner at Improsec/itm8, focusing on offensive security testing and regulatory compliance. In early 2026, he transitioned to the aviation industry, where he today leads a team of cybersecurity specialists safeguarding more than 30 million annual passengers, over 800 daily departures, and more than 10,000 colleagues.more
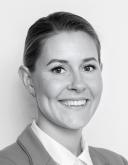
Ann-Sophie Barrington, CISO, JP/Politikens Hus

Maria Christiansen, Head of Applied AI, TDC NET
Maria Christiansen is a deep-tech and AI executive focused on one question: how do we turn breakthroughs in artificial intelligence and quantum technologies into real-world competitive advantage?As Head of Applied AI at TDC NET, she leads strategic AI transformation and explores emerging opportunities in quantum optimization, quantum-secure infrastructure, and advanced... decision intelligence. Drawing on experience across telecommunications, healthcare, logistics, and energy, Maria specializes in bridging the gap between frontier research and commercial impact, helping organizations transform scientific innovation into business reality.more

Ulf Larsson, Security CTO, SEB
Ulf Larsson is Security CTO at SEB, where he focuses on the shift from assumed control to demonstrated cyber resilience.His work centers on how organisations can build security that holds under real operating conditions, as technology changes, dependencies move, AI influences decisions, and traditional governance models come under pressure.Ulf is particularly focused... on making security easier to do right, harder to bypass, and possible evidence. He works across strategy, architecture, risk and execution to help teams reduce ambiguity, challenge assumptions early, and build confidence that the right controls work when it matters.His perspective is simple: security is not what you implement. It is what you can prove.more

Rune Espensen, Head of Information Security Office, Nordea
With nearly 25 years of experience in security, Rune Espensen has built a diverse career spanning software development, enterprise security solutions, and identity and access management consulting. As a global red teamer, he has tested the resilience of everything from cars and electrical grids to banks. Today, Rune brings his deep technical expertise to a strategic... level, overseeing Technology and Information Security topics within Nordea’s risk management function.more
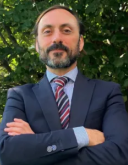
Thomas B. Zuliani, Senior Director, Global IT Security Services, GEA Group
Thomas B. Zuliani is a senior IT and cybersecurity executive with more than 20 years of experience leading information security, technology services, data protection, and organizational transformation across complex global enterprises.He currently serves as Senior Director, Global IT Security Services at GEA Group, where he is responsible for defining and driving... the strategic direction, performance, and continuous evolution of GEA’s global IT Security Services and security infrastructure. He leads the Global IT Security Services organization, delivering secure, scalable, and resilient capabilities that support GEA’s digital transformation and operational excellence.Combining strategic planning, operational excellence, and strong stakeholder engagement, Thomas ensures that security services remain future-ready and closely aligned with business priorities. He owns and evolves the IT Security Services roadmap, strengthening security capabilities in line with GEA’s business objectives, risk posture, and long-term strategy.
Prior to joining GEA, Thomas served as Global CISO at Arla Foods from July 2023 to December 2025, where he led efforts to strengthen cybersecurity and data security across one of the world’s leading dairy organizations. His work focused on building robust defenses against an evolving threat landscape while embedding security more deeply into business operations and supporting broader cybersecurity collaboration.Previously, as Information Security & Data Privacy Director at Pandora, Thomas held leadership responsibility across information security and data privacy, further developing his experience at the intersection of cybersecurity, risk, privacy, technology, and global business.Beyond his corporate leadership roles, Thomas has been active in the wider cybersecurity community, including serving as Co-Chair of the Nordic CISO Community, bringing security leaders together to exchange knowledge, address emerging challenges, and advance the future of information security.At the heart of Thomas’s leadership philosophy is a belief that technology should create tangible business and societal value. His vision is a future in which AI and humans coexist productively—using technology to build a world that is more secure, healthier, environmentally responsible, and energy efficient. He sees IT and cybersecurity not simply as support functions, but as integral components of business strategy that enable innovation, resilience, and sustainable growth.
Equally important is his focus on people. Thomas believes that sustainable high performance is built through trust, motivation, collaboration, and a healthy balance between professional and personal life—creating teams that are both highly effective and equipped to thrive over the long term.more
Jan Jans, Legal Counsel, Finanstilsynet (Danish Financial Supervisory Authority)
Jan Jans is a legal expert specializing in financial cybersecurity at the Danish FSA. He has experience in the Danish implementation of the EU's Digital Operational Resilience Act (DORA) and the NIS2 Directive. His work primarily involves developing and enforcing regulations that govern IT risk management and digital resilience within the financial sector. Jans is... actively involved in further development of the EU- and Danish legislative framework for DORA and preparing the FSA's supervisory approach to new EU digital mandates.more
Laurits Ketscher, Data Protection Officer, Danish Ministry of Finance
As Data Protection Officer for the Danish Ministry of Finance, Laurits leads the Data Protection Officer function across the Ministry and its seven agencies. He serves as an independent advisor to executive leadership, employees, and data subjects on privacy, AI governance, information security, and regulatory compliance, helping ensure the responsible and compliant... use of data and emerging technologies across the organisation.
With a background in law complemented by formal education in information technology, Laurits has held worked and advised across multinational organisations, public-sector institutions, and European bodies. His experience spans AI governance, cybersecurity, privacy, digital risk, and regulatory compliance, enabling organisations to navigate complex technology and regulatory landscapes.more
Tom John Fischer Jensen, Head of Privacy & Security, Semler Gruppen
Tom is specialized in digital compliance & cyber security, aligning both fields with a focus on organizational maturity and business optimization. Tom heads the security and digital compliance division for Semler Gruppen, one of Denmark’s biggest conglomerates. Operating in multiple countries and sectors, Tom excels in managing different compliance programs,... across companies, in different sectors.more
Geoffrey Taylor, Information Security Officer, Nordea Asset Management
Geoffrey Taylor is an information security leader with over two decades of experience shaping cybersecurity strategies across the financial services, technology, manufacturing, and mobility sectors. He specializes in information security strategy risk management, governance, and resilience, and has deep expertise in ISO 27001, NIS2 and DORA. Geoffrey holds CISM,... CRISC, and ISO 27001 Lead Implementer, ISO 42001 Implementer certifications and is a PECB-certified trainer. He is active in the global cybersecurity community and contributes to ISACA, the Cloud Security Alliance, and international mentorship programs.more

Chris Dearden, Lead Sales Engineer, Delinea
Chris has been in IT for over 20 years with a career covering a broad spectrum from Operations to Architecture both in the Datacentre & the Cloud. Chris has spent the last 14 years working within the technical teams at a number of software vendors, including data protection, cloud native security & storage.
Marcus Mølleskov, Chief Risk & Compliance Officer, Januar
Marcus Mølleskov is the Co-Founder and Chief Risk & Compliance Officer at Januar. For +5 years he has worked with Risk and Compliance and the intersection between Crypto and Payments. Before Januar he worked +7 years with financial risk management in two large Danish banks. Marcus is also part of the Danish FinTech Forum hosted by the Danish FSA to discuss... matters of regulation and technology in the Danish Financial Industry and Forum on IT Crime (FIT) hosted by Danish Police to discuss potential PPP efforts to prevent IT related crime. Marcus is also a thought leader in the EU crypto compliance space, having over 8,000 followers on LinkedIn and often speaking on podcasts and at conferences about the intersections between finance and crypto, crypto compliance, crypto payments, stablecoins and financial crime prevention.Januar is licensed by the Danish FSA as a Payment Institution under PSD2 and as a CASP under MiCA. With its dual license Januar is the compliant gateway between traditional finance and crypto for businesses, institutional investors and financial institutions. Januar provides accounts and payment solutions to support its clients to run their business with peace of mind. Januar also provides crypto custody, crypto transfer services, on-/off-ramp solutions and EMT partnership for CASPs and PSPs, which makes Januar a one stop financial partner for all companies dealing with crypto.more
Lars Liljeroth, Solutions Engineer, Netskope
Lars Liljeroth has been working in the IT industry for 20+ years. As a certified expert, he specializes in Security Services Edge (SSE), part of the Secure Access Service Edge (SASE) framework at the core of modern security architecture. As a Solutions Engineer at Netskope, Lars focuses on advising customers and driving technological innovation through practical Zero... Trust principles.more

Magnus Lundgren, Sales Director Nordics, Filigran
Magnus has been in Cyber Security for over a decade and worked closely with some of the largest and most advanced Threat Intelligence teams (private and public) in the world. He is passionate about using technological leadership to solve real problems.
Philip Jacobs, Principal Intelligence Solutions Advisor, Intel 471
Philip Jacobs has been working in intelligence for over 10 years, with a career spanning intelligence analysis, OSINT, threat intelligence, enterprise security and consulting. As Principal Intelligence Solutions Advisor at Intel 471, he works with security teams across the Nordics and wider EMEA / APAC, helping them understand the threat actors targeting their organisation... and how to utilise threat intelligence as a practical, proactive defence. Philip is passionate about cutting through industry hype to focus on the threats that matter.more
Matt Percival, Regional VP of Sales, Horizon3.ai
Ben Hanson, Field CISO, Zenity
Ben Hanson is Field CISO and Director at Zenity. Operating at the cutting edge of agentic AI, he works with CISOs and security teams at the world's most sophisticated organisations, helping them transition from static security controls and guardrails to the fundamentally different challenge of governing intent and agency. Ben is also a leading voice on applying systems... thinking to cybersecurity and AI, a member of Edinburgh University’s respected Gamification and Systems Thinking Lab, and an influential keynote speaker with talks at Cambridge University, Oxford University, Black Hat, ISACA, SANS, Cloud Security Alliance, UK Cyber Security Council, and many others. A 25 year industry veteran, before joining Zenity he was Senior Security Strategist & Advisor at Microsoft, where he advised the leaders of the world’s largest Financial Services institutions, including industry giants such as HSBC, Barclays, Santander, Lloyds Banking Group, Bank of England, London Stock Exchange, and NatWest Group. Prior to Microsoft he led the Cyber practice for a top US management consultancy.
more
Rachel Eldridge, Solutions Engineer, BeyondTrust
Rachel Eldridge is a Solutions Engineer at BeyondTrust, where she helps organisations across the Nordics and Benelux secure privileged access for humans, machines, and AI agents. She works across BeyondTrust’s full identity security portfolio, from Privileged Remote Access and Remote Support to Endpoint Privilege Management and Identity Security Insights. Before... BeyondTrust, she spent several years in distribution, specialising in vendors such as CrowdStrike, Okta, AbnormalAI and ExtraHop.
more
Robin Johns, Worldwide AI Security Subject Matter Expert, Cato Networks
Robin Johns is the Worldwide AI Security Subject Matter Expert at Cato Networks, where he leads global strategy and field engagement for securing AI adoption. With a background spanning cybersecurity, sales engineering, and enablement, Robin works at the intersection of innovation and risk—helping organizations embrace AI while maintaining control, visibility, and... trust.more